
Introduction
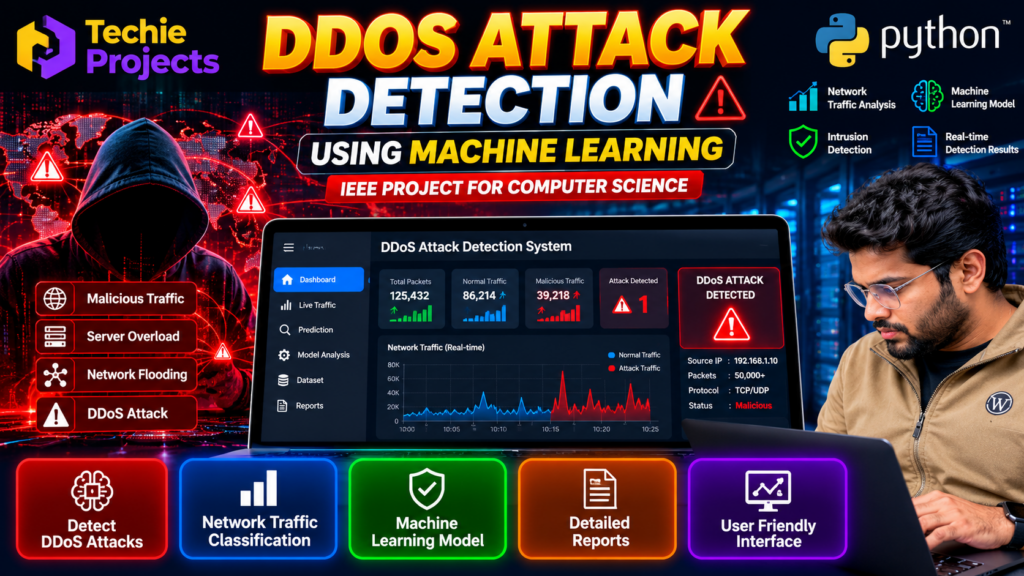
DDoS attack detection using machine learning is a cybersecurity project that focuses on identifying suspicious network traffic and detecting potential Distributed Denial-of-Service (DDoS) attacks. This Python-based project is suitable for B.Tech, B.E., Computer Science Engineering, Information Technology, and cybersecurity students looking for a practical final-year project.
A Distributed Denial-of-Service attack attempts to overwhelm a server, website, or network service with excessive traffic, making it difficult for legitimate users to access the service. Traditional security techniques often rely on predefined rules, while machine learning can help identify traffic patterns associated with potential attacks.
The DDoS attack detection using machine learning project demonstrates how network traffic data can be processed, analyzed, and classified to distinguish normal traffic from potentially malicious activity. It combines Python programming, data preprocessing, machine learning algorithms, and cybersecurity concepts in a practical academic implementation.
🎓 Looking for a cybersecurity project for your final-year submission? Techie Projects can help you explore project implementation options, source code availability, setup requirements, and customization according to your academic needs.
🎬 DDoS Attack Detection Using Machine Learning – Project Demo
Watch the project demonstration to understand the system interface, detection workflow, and key features of the DDoS attack detection application.
The demo helps students understand how a machine learning-based cybersecurity application can analyze network traffic data and display potential attack classifications. Review the demonstration to see whether the project aligns with your final-year requirements.
🎯 Objectives of the Project
The main objectives of this project are:
- Understand the fundamentals of Distributed Denial-of-Service attacks.
- Analyze network traffic data for suspicious patterns.
- Apply machine learning techniques to network traffic classification.
- Develop a Python-based application for demonstrating attack detection.
- Display classification results in a clear and understandable format.
- Explore how machine learning can support network security monitoring.
- Learn the practical implementation of a cybersecurity project.
These objectives make the project useful for students interested in machine learning, networking, information security, and applied artificial intelligence.
🔍 What Is DDoS Attack Detection Using Machine Learning?
DDoS attack detection using machine learning involves training or applying a model to recognize patterns associated with normal and potentially malicious network traffic.
A dataset may contain features such as packet counts, connection duration, protocol information, traffic volume, and other network-flow measurements. The selected features depend on the dataset and model used in the implementation.
After preprocessing, the machine learning model evaluates the input features and produces a classification. Depending on the implementation, the output may indicate normal traffic or suspected attack traffic.
Machine learning does not guarantee that every attack will be detected correctly. Model performance depends on dataset quality, feature selection, training procedures, and how closely real-world traffic resembles the training data.
“The DDoS Attack Detection Using Machine Learning project demonstrates how machine learning techniques can analyze network traffic and identify patterns associated with distributed denial-of-service attacks. This Python-based cybersecurity project helps students understand traffic classification, data preprocessing, model evaluation, and intrusion detection concepts.”
⚙️ How Does the Project Work?
The typical workflow of a DDoS attack detection system includes the following stages.
1. Network Traffic Dataset Collection
The project begins with a suitable dataset containing network traffic records. A labeled dataset may include examples of normal traffic and different attack categories.
For an academic implementation, publicly available cybersecurity datasets can be considered after checking their licensing, format, and suitability for the project.
2. Data Preprocessing
Raw data may contain missing values, duplicate records, inconsistent formats, or features that are not suitable for direct model input.
Preprocessing prepares the dataset for analysis. Depending on the dataset, this stage may include handling missing values, encoding categorical features, scaling numerical values, and removing irrelevant columns.
3. Feature Selection
Feature selection identifies the network traffic attributes that may help the model distinguish normal behavior from attack patterns.
Selecting appropriate features can simplify model training and help students understand which traffic characteristics influence classification.
4. Machine Learning Model Training
The processed dataset can be used to train a suitable classification model. Depending on the project implementation, algorithms such as Random Forest, Decision Tree, Logistic Regression, or Support Vector Machine may be considered.
The algorithm should be selected according to the dataset, performance requirements, and project scope rather than assuming one method will always provide the best results.
5. Traffic Classification
After training, the model receives appropriately formatted input features and predicts a traffic category.
The application may display the prediction as normal traffic or suspected DDoS traffic, depending on the classes supported by the model.
6. Result Display and Evaluation
The system displays the prediction through a console, graphical interface, or dashboard, depending on its implementation.
Students can evaluate the model using metrics such as accuracy, precision, recall, F1-score, and a confusion matrix. These metrics provide a more complete view of performance than accuracy alone.
🚀 Features of DDoS Attack Detection Using Machine Learning
The following features can be included according to the selected implementation.
📊 Network Traffic Analysis
Analyze structured network traffic records to identify characteristics that may be associated with suspicious activity.
🤖 Machine Learning-Based Classification
Use a trained classification model to predict whether an input record belongs to a supported normal or attack category.
🛡️ Cybersecurity Learning
Explore traffic analysis, attack detection, classification, and basic network security concepts through a practical Python project.
📈 Performance Evaluation
Evaluate the model using classification metrics and test data. This helps students explain the strengths and limitations of their approach during a project presentation.
💻 Python-Based Implementation
Python provides widely used libraries for data processing, machine learning, and visualization, making it suitable for an academic cybersecurity application.
🧩 Extendable Project Structure
Depending on the codebase, students may extend the project with additional datasets, more traffic categories, visualizations, or a web-based interface.
Important: A dataset-based classifier is not automatically a live network protection system. Real-time packet capture, deployment, automated blocking, and production-grade monitoring require additional implementation and testing.
🛠️ Technologies Used
A typical implementation may use the following technologies:
- Programming language: Python
- Data processing: Pandas and NumPy
- Machine learning: Scikit-learn or another compatible ML framework
- Visualization: Matplotlib or Seaborn, if required
- User interface: Tkinter, Streamlit, Flask, or a console interface, depending on the implementation
- Dataset: A suitable labeled network traffic dataset
The exact technology stack depends on the available project version. Confirm the included libraries and supported software versions before installation.
💻 Software and Hardware Requirements
Software Requirements
- Python installed in a compatible version
- Windows, Linux, or another supported operating system
- Required Python libraries
- A code editor such as Visual Studio Code or PyCharm
- The dataset used by the implementation
Hardware Requirements
- A computer or laptop capable of running Python
- Adequate RAM for loading and processing the dataset
- Sufficient disk space for the source code, libraries, and dataset
- An internet connection for downloading dependencies, if required
A GPU is not necessarily required for a traditional machine learning classifier. Hardware requirements depend on dataset size and the algorithms used.
📚 Why Choose This Project for Your Final Year?
A DDoS attack detection using machine learning project connects theoretical cybersecurity concepts with practical data analysis.
1. Practical Machine Learning Experience
Students can learn the relationship between dataset preparation, model training, prediction, and performance evaluation.
2. Cybersecurity Knowledge
The project introduces network attacks, suspicious traffic patterns, and the role of data-driven approaches in security monitoring.
3. Suitable for Technical Demonstrations
The project can be demonstrated using sample traffic records, model predictions, evaluation metrics, and an interface when included.
4. Scope for Further Development
Students can explore additional traffic datasets, compare multiple classification algorithms, or develop a dashboard to present results.
5. Useful for Project Documentation
The workflow provides material for explaining the problem statement, objectives, methodology, architecture, implementation, testing, results, and future scope in an academic report.
🛒 Get the DDoS Attack Detection Project from Techie Projects
Need a ready-to-explore cybersecurity project for your final-year academic work?
Techie Projects helps students explore Python, machine learning, artificial intelligence, and cybersecurity project options. Contact us to confirm the availability and exact contents of the DDoS attack detection project before placing an order.
Depending on the selected package and availability, you can enquire about:
- Project source code and setup instructions
- Guidance for running the application
- An explanation of the implementation and workflow
- Project customization based on your academic requirements
- Assistance understanding the model and evaluation results
- Documentation or other deliverables, where included in the selected package
The deliverables, support, pricing, and customization options should be confirmed before purchase.
📲 Request Project Details
Interested in this DDoS attack detection using machine learning project? Contact Techie Projects to ask about availability, pricing, source code, and customization.
- 📲 Call/WhatsApp: +91-9460060699
- 🌎 Website: www.techieprojects.com
- 📺 Instagram: @pythonprojects_
Send your course, semester, submission deadline, and required features so that the available project options can be discussed.
🔮 Future Scope
The project can be extended in several directions, subject to the available source code and technical requirements.
- Multiple attack categories: Train and evaluate the model on datasets containing different types of network attacks.
- Dashboard visualization: Display traffic statistics and model evaluation results in a graphical dashboard.
- Algorithm comparison: Compare multiple classifiers using the same evaluation procedure.
- Improved data handling: Test preprocessing and feature-selection approaches to understand their effect on model performance.
- Real-time analysis: Explore traffic-stream integration in an isolated, authorized test environment.
- Alert integration: Add notifications for suspicious predictions if the application supports an appropriate monitoring workflow.
These extensions are development possibilities, not features guaranteed to be present in the current project.
⚠️ Project Limitations
Understanding limitations is an important part of a credible engineering project.
- Performance depends on the dataset and model quality.
- Traffic patterns can change over time, potentially reducing model reliability.
- False positives may classify legitimate traffic as suspicious.
- False negatives may allow attack traffic to go undetected.
- Dataset-based predictions do not prove that a live network is protected.
- Real-world deployment requires additional security testing, monitoring, and operational safeguards.
Students should report measured results from their actual implementation rather than claiming unverified accuracy or guaranteed attack prevention.
❓ Frequently Asked Questions
1. What is a DDoS attack detection using machine learning project?
It is a cybersecurity application that uses machine learning to classify network traffic and identify patterns associated with potential Distributed Denial-of-Service attacks.
2. Which programming language is used?
Python is commonly used for this type of project because it provides libraries for data preprocessing, model development, and evaluation.
3. Is this project suitable for B.Tech final-year students?
Yes. It can be suitable for Computer Science, Information Technology, and cybersecurity students, depending on their syllabus, project requirements, and implementation scope.
4. Which machine learning algorithms can be used?
Possible choices include Random Forest, Decision Tree, Logistic Regression, and Support Vector Machine. The most appropriate model depends on the dataset and evaluation results.
5. Can I customize the project?
Customization may be possible depending on the available codebase and requirements. Contact Techie Projects to confirm the scope, feasibility, timeline, and cost.
6. Does the project detect live DDoS attacks automatically?
Not necessarily. A dataset-based implementation may classify prepared records only. Live monitoring requires additional traffic collection, integration, and testing.
7. How can I purchase this project?
Contact Techie Projects through WhatsApp at https://wa.me/919460060699 to ask about availability, pricing, deliverables, and support before ordering.
🎓 Explore Related Projects
Explore these related areas for more final-year project ideas:
- Network Intrusion Detection System
- Phishing Website Detection Using Machine Learning
- Malware Detection Using Machine Learning
- Intrusion Detection Using the NSL-KDD Dataset
- Cybersecurity Anomaly Detection Using Python
Visit the Techie Projects website to explore available project categories and enquire about relevant implementations.
✅ Conclusion
DDoS attack detection using machine learning is a useful academic project for students interested in Python programming, network security, and machine learning. It provides an opportunity to study traffic data, train a classification model, evaluate predictions, and understand the challenges involved in detecting suspicious network activity.
For students seeking a practical final-year project, Techie Projects can help clarify available source code, setup requirements, customization options, and purchase details.
Ready to explore this project? Contact us through WhatsApp or visit Techie Projects to discuss your academic requirements and available project options.